Dr. Frederick A. Smith, Founder & CEO
Experience forged in public service, military operations, and the practical demands of securing mission-critical systems.
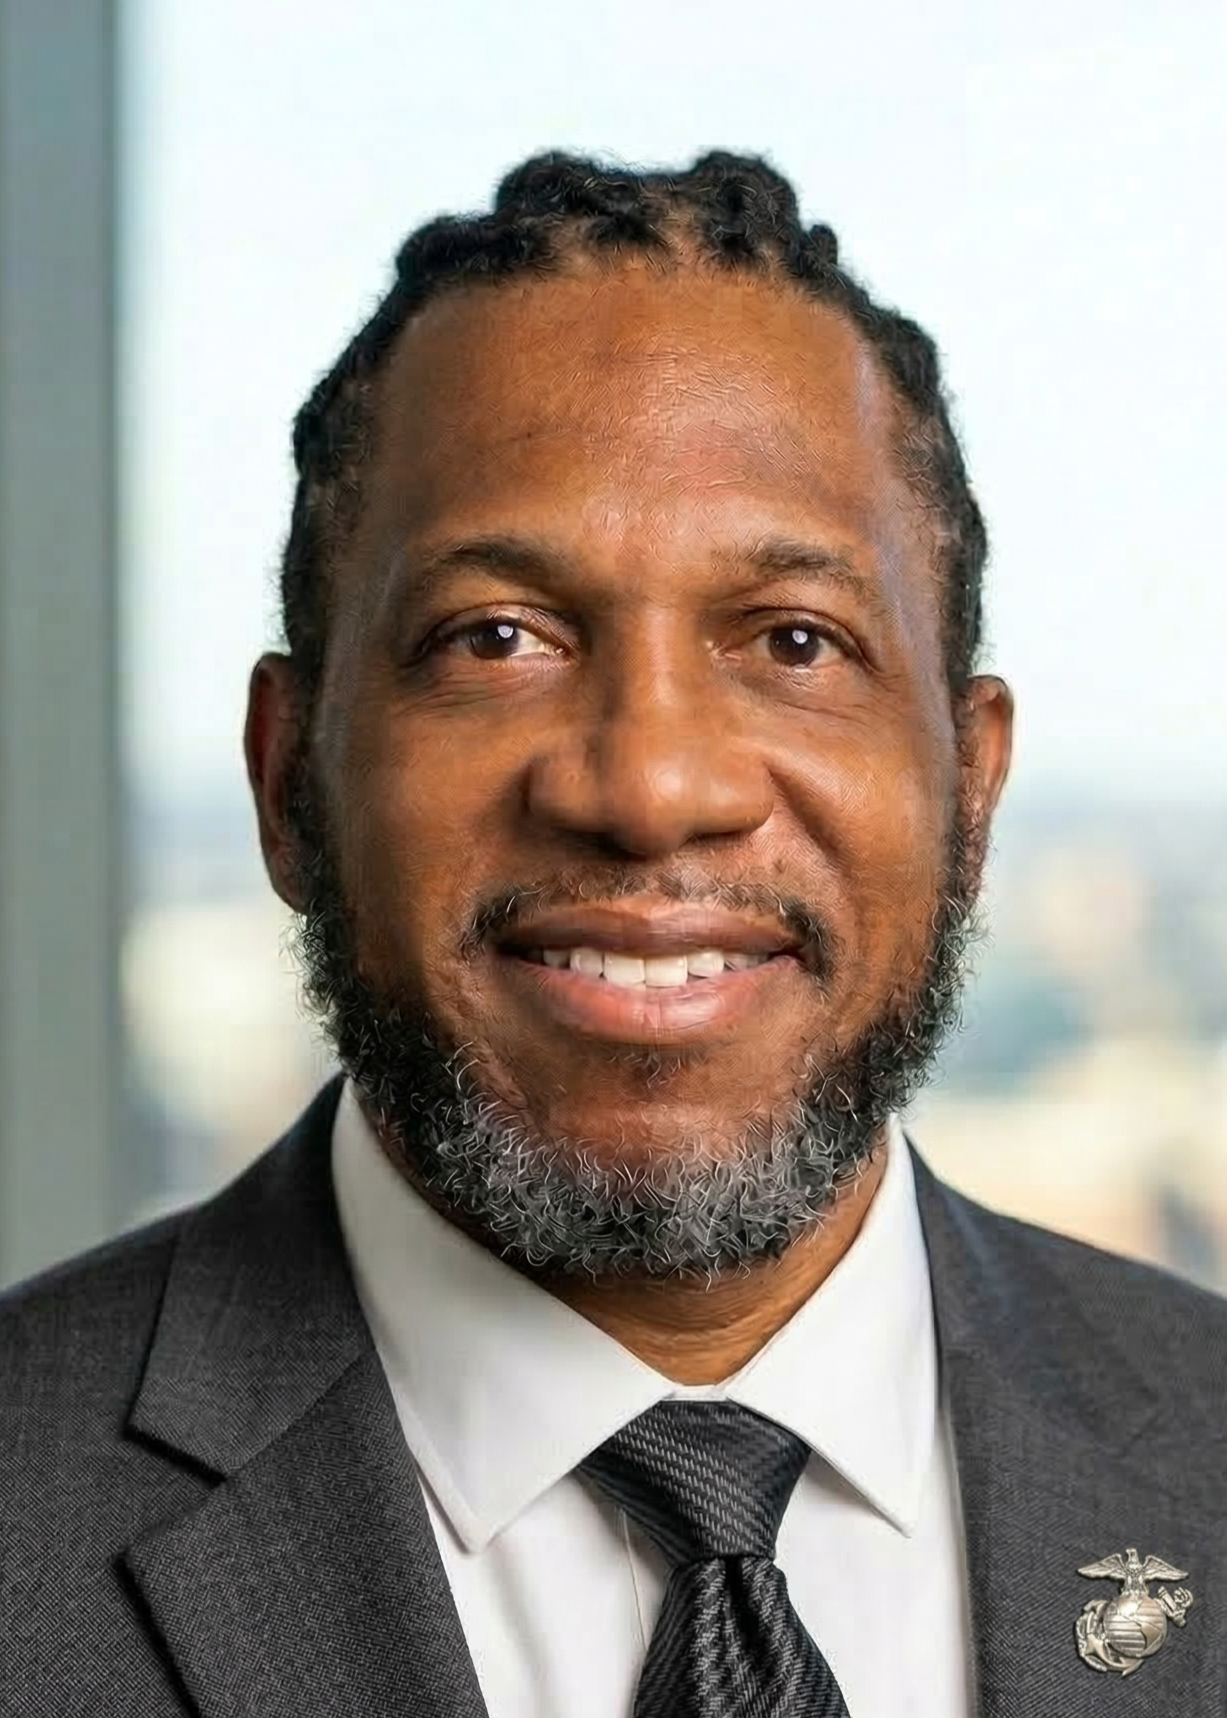
Dr. Frederick A. Smith
More than 35 years of leadership where technology, security, and mission execution intersect.
Dr. Smith founded NRSFAS Corporation on a conviction formed over decades of military, federal, and defense-sector service: organizations need more than technically sound plans. They need disciplined leaders who can turn complex requirements into secure, dependable operational results.
From leading Marine Corps communications teams to overseeing federal cybersecurity programs and technical testing, he has worked in settings where readiness, risk, and accountability have immediate consequences. His experience spans secure information systems, enterprise operations, engineering, acquisition support, and multidisciplinary workforce leadership.
In his ongoing role as Test Director, he provides critical support to the Marine Corps Tactical Systems Support Activity. He also teaches cybersecurity, information security, and cloud computing as adjunct faculty at Central Texas College. Together, these operational and academic perspectives inform how NRSFAS serves its customers.
Measured Results in Demanding Environments
Selected outcomes from Dr. Smith’s prior operational and leadership assignments demonstrate a consistent emphasis on reliability, security, and process improvement.
97%+
Information-system readiness sustained during military operational service.
99.7%
System availability supported in demanding defense technical operations.
21%
Fewer open cybersecurity Plans of Action and Milestones in Navy work.
25%
Shorter end-to-end processing cycles in a federal program environment.
A Career Built Around Readiness
His leadership experience crosses the full spectrum from deployed communications and federal systems governance to the evaluation of next-generation tactical capabilities.
Marine Corps Tactical Systems Support Activity
As a Test Director, Dr. Smith coordinates technical test events involving command-and-control, communications, cyber, intelligence and reconnaissance capabilities, and littoral platforms. His work connects requirements, test evidence, interoperability, and risk analysis to decisions about system performance and fielding.
He works across government and contractor disciplines and applies structured risk assessment, including Failure Modes and Effects Analysis.
Federal Technology Leadership
At the U.S. Department of Housing and Urban Development, he advised senior leaders on enterprise systems, cybersecurity governance, data quality, and process improvement. His work included NIST-informed practices, Zero Trust principles, Microsoft Sentinel, and Microsoft Defender technologies.
At the Department of the Navy, he led technical teams responsible for cybersecurity governance, Risk Management Framework execution, security authorization, and aviation-program support.
Defense & Expeditionary Operations
Through roles with Leidos, SAIC, and L-3 Communications, he managed technical operations in austere and deployed environments. The work encompassed secure networks, classified communications, biometrics, surveillance infrastructure, continuity, and high-availability support.
These assignments developed a practical understanding of technical dependencies under demanding operating conditions.
United States Marine Corps
As a Gunnery Sergeant and Communication Information System Manager, Dr. Smith led personnel delivering tactical communications and information systems across operational theaters in the Asia-Pacific and Southwest Asia.
His responsibilities included operational readiness, contingency planning, disaster recovery, logistics, training, and the development of military personnel.
Technical Depth, Operational Perspective
Cybersecurity Governance
NIST Risk Management Framework and SP 800-53 controls, Assessment and Authorization, continuous monitoring, vulnerability management, incident response, and Zero Trust principles.
Enterprise & Cloud Security
Experience with Microsoft Sentinel, Defender security technologies, Azure Log Analytics, identity protection, system administration, and resilient infrastructure.
Systems Test & Engineering
Requirements traceability, test execution, technical analysis, hardware and software integration, interoperability testing, and evidence supporting acquisition decisions.
Knowledge Shared, Not Just Applied
Dr. Smith earned a PhD in Information Technology and Cybersecurity from Capella University. His dissertation, The Influence of Anonymity Factors on IT Security Incident Reporting, examined how trust, perceived personal risk, and anonymity shape security-reporting behavior.
His research reinforces a central theme of his leadership: effective cybersecurity depends on people, organizational culture, and clear processes as well as technical controls. He brings this perspective into the classroom as an adjunct instructor at Central Texas College.
Academic Qualifications
- PhD, Information Technology & Cybersecurity — Capella University
- MS, Information Technology — Florida Institute of Technology
- MBA — National University
- BS degrees, Human Resources Management and Social Psychology — Park University
- Master certificates, Information Security Management and IT Project Management — Villanova University
Selected Professional Credentials
- FAC-P/PM Senior Level, IT Specialization
- Defense Acquisition Corps professional member and DAU qualifications
- CompTIA Security+ (CE), CompTIA Server+, and ITIL v3
- Lean Six Sigma Green Belt and Scrum Master
- OSHA Authorized General Industry Trainer
The Principles Behind NRSFAS
Dr. Smith’s leadership model reflects decades of responsibility for people, systems, security, and results in environments where performance matters.
Mission Readiness First
Start with operational needs, then align security, technology, people, resources, and performance measures.
Compliance by Design
Integrate security, quality, testing, documentation, and audit evidence throughout delivery.
Visible, Managed Risk
Identify, assess, mitigate, track, and communicate risks rather than treating them as an afterthought.
Evidence-Based Decisions
Support customer confidence with requirements traceability, test findings, corrective actions, and documented results.
Measurable Resilience
Manage readiness, uptime, cybersecurity exposure, schedule performance, and service quality through meaningful metrics.
Servant Leadership
Develop professionals, remove obstacles, establish accountability, and equip teams to succeed.
Ready to Support the Next Requirement
NRSFAS Corporation welcomes conversations with government organizations, prime contractors, and prospective teaming partners seeking support in cybersecurity, information technology operations, systems testing, infrastructure, engineering, compliance, and program delivery capabilities.
As a Service-Disabled Veteran-Owned Small Business and California-certified Small Business and Disabled Veteran Business Enterprise, NRSFAS combines responsive small-business delivery with leadership informed by federal and defense operations. Review our contracting pathways or contact our team to discuss qualifications, capability statements, subcontracting, and teaming opportunities.